Security built into every layer

Circuit protects your information through secure infrastructure, enterprise access controls, and responsible data practices.

SOC 2 Type II audited
Trusted by

Protecting your business-critical information

Secure infrastructure

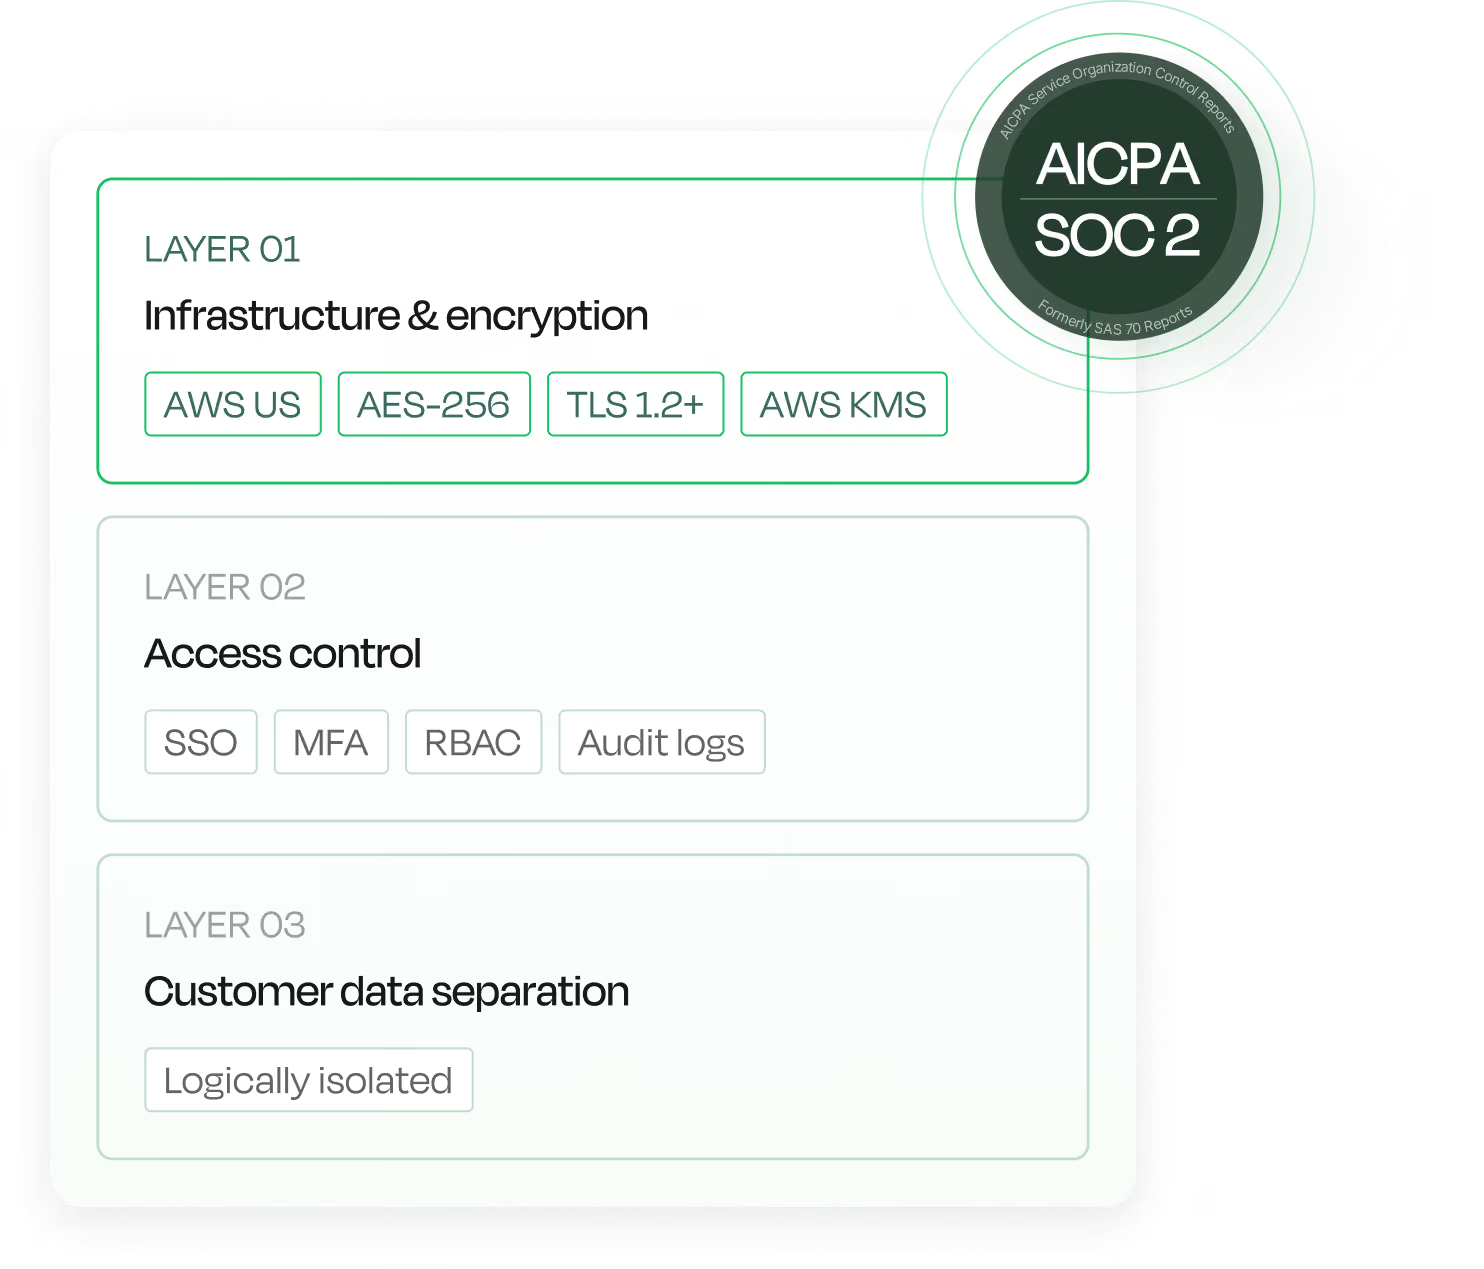
Circuit has achieved SOC 2 Type II compliance, verified through independent audit. Customer information is encrypted at rest using AES-256 and in transit using TLS 1.2 or higher. Encryption keys are managed and rotated using AWS Key Management Service (KMS).

Your information stays yours

Each customer's information is logically isolated within the platform to prevent cross-tenant access and ensure your organization's information remains separate from every other customer.

Control access across your organization

Single sign-on (SSO)

Support for Microsoft and Google single sign-on (SSO), with multi-factor authentication (MFA), lets users authenticate using existing enterprise credentials. New accounts are created automatically on first sign-in through just-in-time (JIT) provisioning, removing the need for manual setup.

Role-based permissions

Circuit uses role-based access controls (RBAC) to manage who can access information across teams, distributors, dealers, franchisees, and external partners. Connected systems respect existing permissions, so users only see the content they're already authorized to access.

Our security practices

Secure development

Security is integrated throughout our software development lifecycle (SDLC), with security reviews built into how we design, build, and release the platform. Circuit is hosted in AWS US regions.

Monitoring & response

We continuously monitor our environment, conduct regular third-party penetration testing, and maintain documented incident response procedures. If customer information is affected, impacted customers are notified in accordance with our contractual and regulatory obligations.

Frequently Asked Questions

How is customer data protected?

Customer data is encrypted at rest using AES-256 and in transit using TLS 1.2 or higher. Encryption keys are securely managed and regularly rotated using AWS Key Management Service (KMS).

Where is customer data stored?

Customer data is hosted in AWS US regions within a SOC 2 Type II audited environment.

Are you SOC 2 compliant?

Yes. Circuit has achieved SOC 2 Type II compliance.

Who can access customer data?

Access is restricted to authorized personnel on a least-privilege, need-to-know basis. Internal access is protected through role-based controls, secured with single sign-on (SSO) and multi-factor authentication (MFA), and logged for auditing.

How is customer data isolated?

Each customer's data is logically isolated to prevent cross-tenant access, ensuring organizations cannot access one another's information.

Do you use customer data to train AI models?

Customer data is not used by third-party AI providers to train their models.

How do you improve the accuracy of AI responses?

Circuit grounds AI responses in your organization's information using retrieval-based techniques. Source attribution and validation measures help users verify responses and support informed decision-making.

What authentication methods do you support?

Circuit supports Microsoft and Google single sign-on (SSO). New user accounts are created automatically on first sign-in, eliminating the need for manual provisioning.

What access controls are available?

Circuit uses role-based access controls (RBAC) to manage access across users, teams, and external partners. When connecting systems like Google Drive, Circuit preserves existing permissions so users can only access the files and information they're already authorized to view.

What happens if there's a security incident?

Circuit maintains a documented incident response process covering detection, containment, recovery, and post-incident review. If customer information is affected, impacted customers are notified in accordance with our contractual and regulatory obligations.